ITT565 · Network OS & Administration
TechSolutions network↗
A group project designing an enterprise intranet for a headquarters and branch office. It combines Packet Tracer topology work, VLAN segmentation, network services, a VPN, and security monitoring.
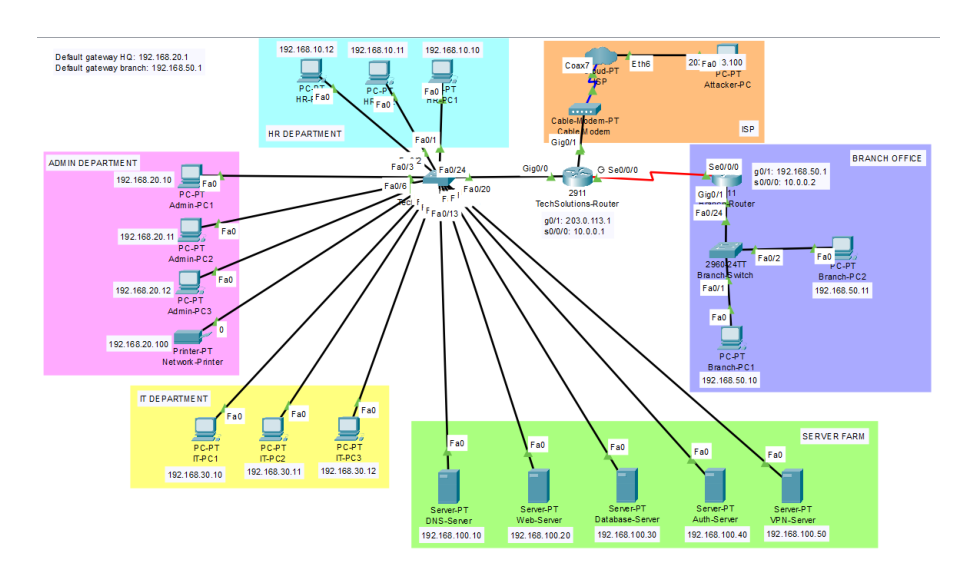
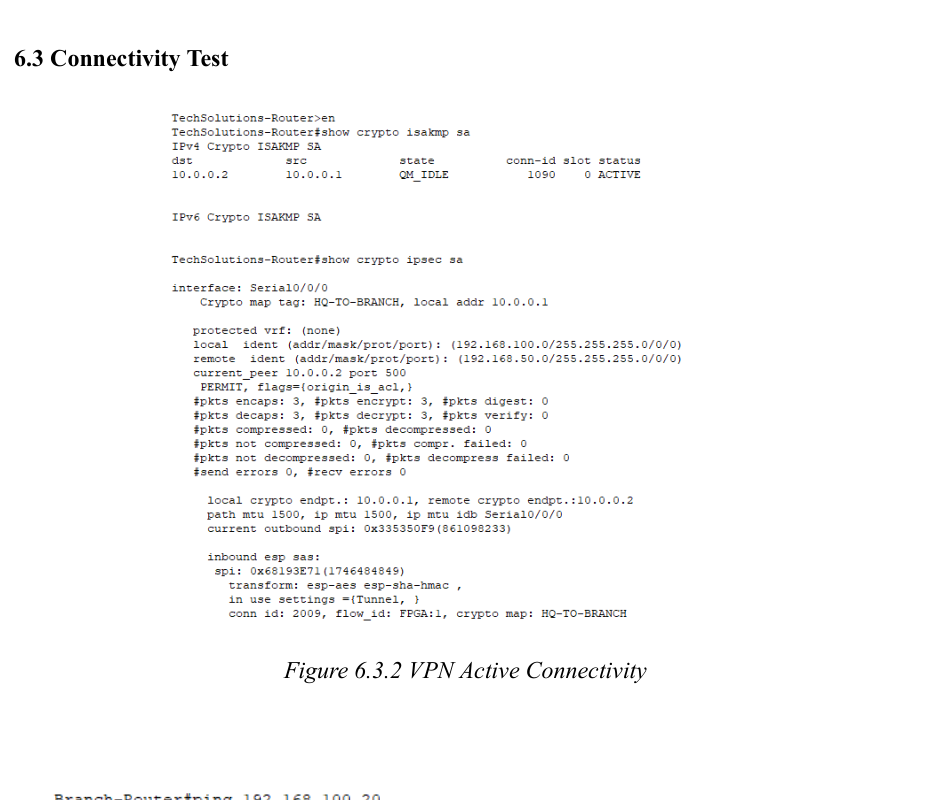
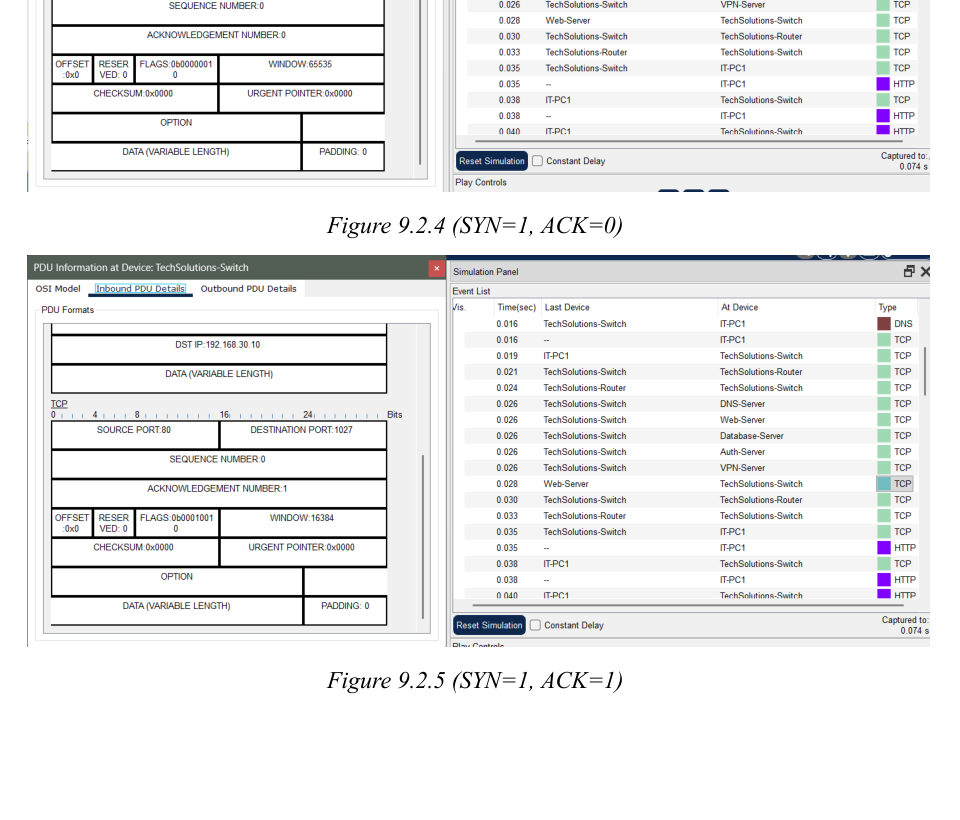
These are figures from the actual project report, not a newly invented topology. The Packet Tracer file and server lab run locally. Report captures document that submission; they are not fresh tests.
THE IDEA
what’s the project?
The report describes departmental VLANs, a server segment, router-on-a-stick inter-VLAN routing, and a headquarters-to-branch connection. The wider team project includes DNS, a web portal, database services, and authentication.
MY INVOLVEMENT
where I came in.
The report names me as VPN & Security Analyst, responsible for VPN deployment, security breach simulation, and Wireshark attack-traffic analysis. Other team members owned DNS/policies, web development, and server administration.
UNDER THE HOOD
how it connects.
Cisco Packet Tracer for network simulation, with server/service administration and Wireshark analysis documented in the report. The VPN configuration section describes an IPsec site-to-site tunnel.
- The topology uses departmental VLANs and a dedicated server subnet.
- The report documents IPsec Phase 1/Phase 2 settings, crypto maps, and static routes for the site-to-site VPN.
- Security analysis connects controlled lab attack activity with captured network traffic and mitigation discussion.
Lab notes +
The role table calls the VPN task OpenVPN, while the detailed configuration describes IPsec. This case study follows the documented IPsec implementation and leaves that discrepancy explicit. The topology has not been reopened or retested here; intermediate Packet Tracer filenames also mention branch connectivity problems.
IN THE ORIGINAL LAB
a quick walkthrough.
- Open the final Packet Tracer topology and inspect headquarters, branch, VLANs, and server segments.
- Verify local and inter-VLAN connectivity, then examine the VPN peers, routes, and security associations.
- Generate traffic between the intended sites and inspect tunnel counters.
- In the isolated security lab, review the report’s packet capture evidence and explain the corresponding mitigations.